Catawba County, North Carolina recently recovered from a ransomware incident without paying the attackers. Their success came from following established incident response procedures, not luck.
Most agencies facing ransomware feel trapped. Systems are down, residents can't access services, and attackers demand payment with a deadline. But agencies that prepare in advance have options beyond writing a check to criminals.
Why You Don't Want to Pay Ransom
Paying ransom doesn't guarantee recovery. Attackers may provide a faulty decryption tool, demand more money, or simply disappear after payment. Your data may still be corrupted or incomplete after decryption.
Payment marks your agency as a willing payer, making you a target for future attacks. It also funds criminal operations that will attack other agencies and businesses.
There are legal and ethical concerns as well. Some ransomware groups are sanctioned entities, making payment potentially illegal. Using taxpayer money to fund criminal enterprises raises obvious questions.
What Makes Recovery Without Payment Possible
Recovery without ransom requires specific capabilities in place before an attack happens.
Working backups stored offline. This is the single most important factor. Your backups must be disconnected from your network or stored in immutable cloud storage that attackers cannot encrypt or delete. Test restoration regularly, not just backup completion.
An incident response plan that staff have practiced. Written plans that sit in a drawer don't help during a crisis. Your team needs to know their roles, have contact information for vendors and law enforcement, and understand the decision tree for different scenarios.
Network segmentation that limits spread. When ransomware enters your network, segmentation prevents it from reaching every system. Critical systems should be isolated so that compromising a workstation doesn't mean compromising your entire infrastructure.
Current asset inventory and system documentation. You need to know what systems you have, how they connect, and what depends on what. Without this, recovery becomes guesswork about which systems to restore first and how they fit together.
The Recovery Process
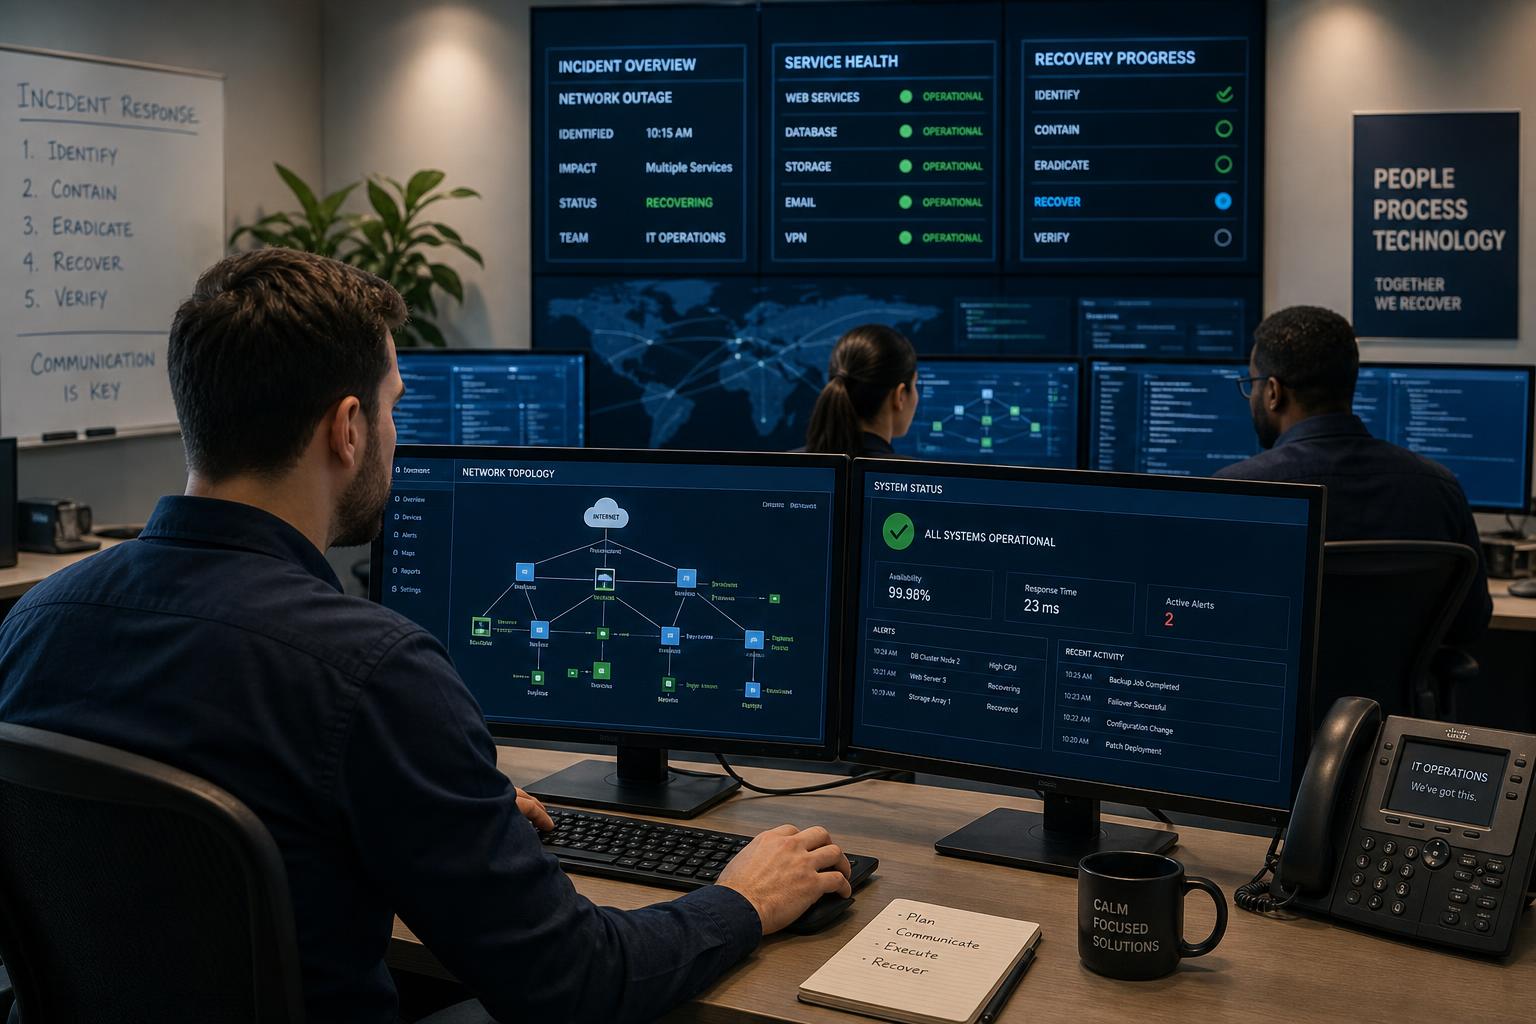
Recovery from ransomware without paying follows a consistent pattern.
First, contain the incident. Disconnect affected systems to prevent further spread. This may mean taking systems offline manually or at the network level. Quick containment limits damage.
Second, identify the scope. Determine what was encrypted, what was accessed, and whether attackers are still in your network. This often requires forensic help from outside specialists who can analyze logs and identify attacker tools.
Third, eliminate attacker access. Remove malware, close the entry point, reset credentials, and apply security updates. Restoring systems while attackers still have access just gives them another chance.
Fourth, restore from clean backups. Start with critical services based on your recovery priority list. Verify that restored systems are clean before reconnecting them to your network.
Fifth, monitor for reinfection. Attackers sometimes maintain persistence through secondary access points. Close monitoring in the weeks after recovery catches problems early.
Building Your Recovery Capability
Start with your backup system. Verify that backups are actually offline or immutable. Check that your backup window captures all critical data. Test full restoration, not just individual files.
Document your incident response procedures. Include specific steps for isolation, who makes decisions about major actions, contact information for your IT vendor and cyber insurance carrier, and communication templates for staff and the public.
Practice your response. Run tabletop exercises where your team walks through a ransomware scenario. Identify gaps in your plan. Update contact lists and procedures.
Review your cyber insurance policy. Understand what it covers, what documentation it requires, and how quickly you can access incident response resources. Many policies include access to forensic specialists and legal counsel.
The Role of Your IT Partner
Agencies that recover successfully often have strong relationships with their IT providers before an incident occurs. Your IT partner should know your systems, have administrative access already established, and understand your priorities.
During an incident, response time matters. An IT partner who has to spend hours learning your environment before they can help will slow recovery. Someone who already manages your systems can act immediately.
Your IT provider should also be part of your prevention strategy. Regular security updates, network monitoring, email filtering, and security awareness training all reduce the likelihood that ransomware succeeds in the first place.
What to Do Now
Review your last backup test. If you haven't done a full restoration test in the past six months, schedule one.
Verify that your backups are truly offline or immutable. If your backup storage is always connected to your network, attackers can encrypt it along with everything else.
Check that you have an incident response plan that includes specific procedures and contact information. If your plan is generic or outdated, update it.
Talk with your IT provider about your recovery capabilities. Make sure they understand your environment and priorities before you need emergency help.
Ransomware attacks on government agencies are common enough that preparation is not optional. Catawba County's recovery shows that agencies with the right preparation can restore operations without funding criminal enterprises. The capabilities that make that possible need to be in place before an attack, not assembled during a crisis.
Not sure your IT is as solid as it should be? Take 10 minutes and tell us about your setup. No pressure, no obligation.
Book a 10-Minute Discovery Call →Last updated: October 14, 2026