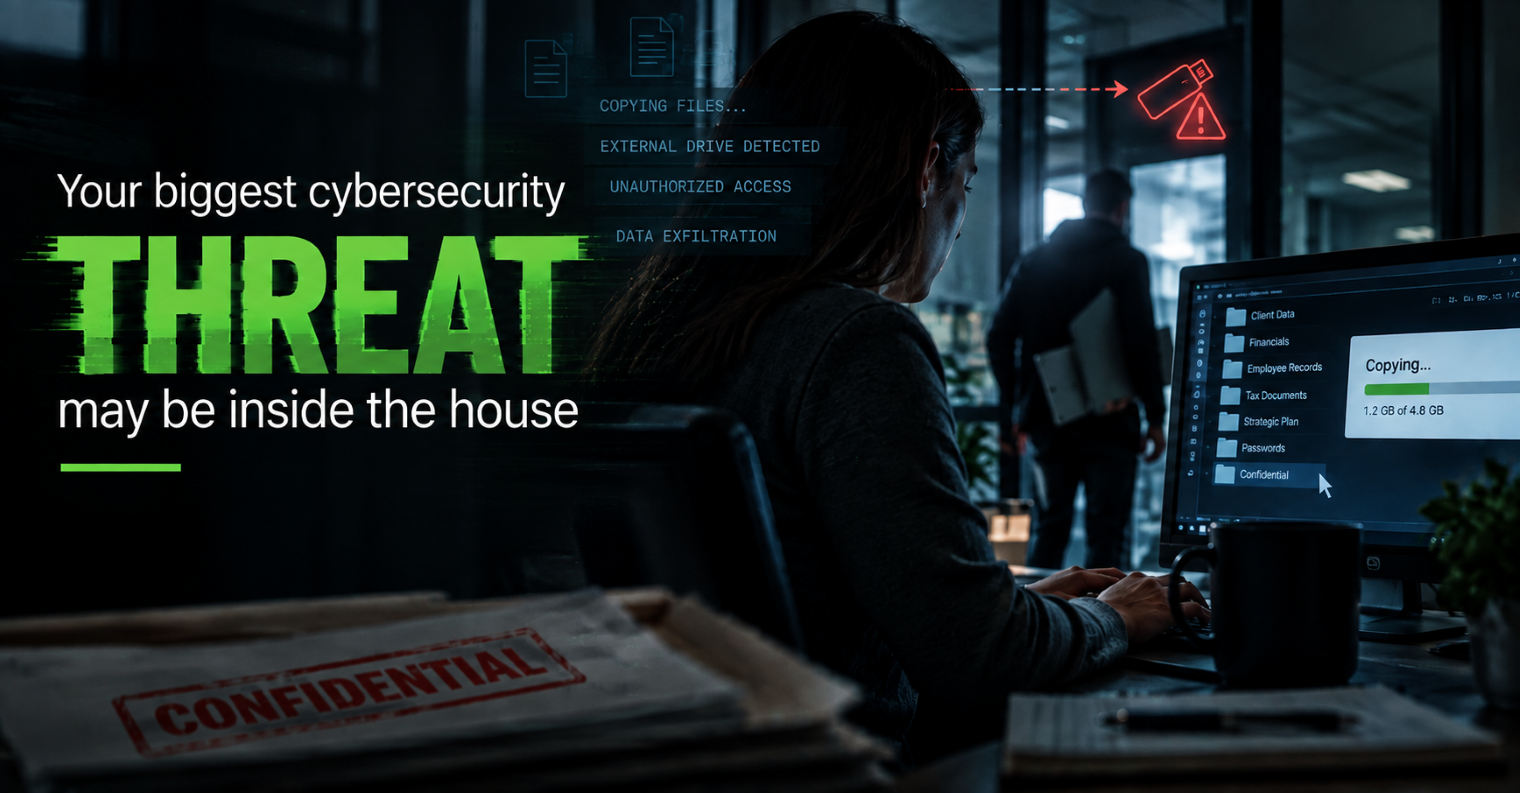
Most business owners picture a hacker in some far-off country when they think about a breach. Someone hunched over a keyboard, working through your firewall line by line.
I get it. It's the version that shows up in movies. It's also, in my experience, not usually how it goes.
A lot of the damage I see starts closer to home. An employee. A vendor. Sometimes a partner who's had access for years and nobody thought to double check. It isn't always malicious. Plenty of it is somebody moving fast and skipping a step they didn't know mattered. Either way, the cost is the same.
The six ways this shows up
Data theft. Someone downloads or copies information they shouldn't have, then walks off with it: a client list, financials, whatever's useful. Doesn't have to be digital. A stolen laptop counts too.
Sabotage. This one's usually personal. A disgruntled employee, or someone who's already decided they're leaving and wants to leave a mark: deleted files, locked accounts, a system that suddenly doesn't work right.
Unauthorized access. Somebody looks at information they had no reason to see. Sometimes it's deliberate. Just as often, it's an employee who didn't realize they'd wandered somewhere they shouldn't have.
Negligence. No bad intent here at all. Someone mishandles a file, ignores a protocol they found annoying, or just makes a mistake. The exposure looks the same either way.
Credential sharing. I compare this to handing a spare house key to someone you like well enough but don't fully trust. Once a password's out of your hands, you don't get to decide what happens to it next.
Unapproved AI use. This one's newer, and I'm seeing it constantly now. An employee pastes a client contract into a free AI tool to "summarize it real quick," and that data's gone. Out of your control, sitting on a server you have no visibility into.
What to watch for
None of these show up with a warning label. But there are patterns worth training your team to notice:
- Someone accessing information that has nothing to do with their job
- A sudden spike in data being downloaded or moved to external drives
- Repeated requests for access nobody can justify
- Company data showing up on a personal laptop or phone
- Antivirus or firewall settings getting disabled
- Sensitive information getting pasted into ChatGPT, Claude, or similar tools without approval
- An employee who's suddenly missing deadlines, acting cagey, or clearly under a lot of stress
One of these alone doesn't mean much. A few of them together, over a short window, is worth a conversation.
Where to start
I tell clients the same five things regardless of size:
- Require MFA everywhere you can turn it on, and get past the "just a password" mindset for good.
- Give people access to what their job requires and nothing more, and review it on a schedule instead of only when someone leaves.
- Train your team on this stuff directly, including what is and isn't okay to do with AI tools. Most people want to do the right thing. They just haven't been told what it is.
- Back up your data in a way that gets tested, instead of scheduled and forgotten.
- Write down what happens if something goes wrong. Skip the binder nobody reads and make it a plan people can follow at 7am when something's already on fire.
You don't have to sort this out solo
I built safemode IT in Kyle because businesses along this stretch of I-35 kept getting the same runaround from IT companies an hour away who didn't know them and didn't especially want to. Insider risk is one of those things that's easy to put off until it isn't. Most owners don't think about it until something's already gone sideways.
If you want a second set of eyes on where you stand, call me at 512-761-7652 or grab time at safemodeit.com/contact. There's no pitch, just a real look at what you've got.
Not sure your IT is as solid as it should be? Take 10 minutes and tell us about your setup. No pressure, no obligation.
Book a 10-Minute Discovery Call →Frequently asked questions
What is insider cybersecurity risk?
It's damage that starts with someone who already has access: an employee, a vendor, or a partner. It isn't always malicious. A lot of it is someone moving fast and skipping a step they didn't know mattered, and the cost to the business is the same either way.
What are the most common types of insider threats?
Data theft, sabotage, unauthorized access, negligence, credential sharing, and unapproved AI use. The last one is newer: an employee pastes a client contract into a free AI tool to summarize it, and that data is now sitting on a server you have no visibility into.
What are the warning signs of an insider threat?
Someone accessing information unrelated to their job, a sudden spike in data being downloaded or moved to external drives, repeated access requests nobody can justify, company data showing up on personal devices, and antivirus or firewall settings getting disabled. One of these alone doesn't mean much. A few together over a short window is worth a conversation.
How do I reduce insider risk in a small business?
Require MFA everywhere you can, give people access only to what their job requires and review it on a schedule, train the team on what is and isn't okay to do with AI tools, back up your data in a way that gets tested, and write down a plan people can follow when something goes wrong.
Can safemode IT help us get a handle on insider risk?
Yes. We're based in Kyle and work with businesses along this stretch of I-35, and the five steps above are where we start with every client, regardless of size. Learn more about our cybersecurity services or call 512-761-7652 for a second set of eyes on where you stand.
Last updated: September 11, 2026