A recent security incident at Frontline Education affected multiple Texas school districts, exposing employee information. The breach happened at the software vendor, not at the schools themselves.
This pattern repeats constantly across healthcare. Your organization protects patient data carefully, but what about the payroll system vendor? The appointment scheduling platform? The billing service? Each one holds sensitive information, and each one is a potential breach point.
Your Vendors Are Your Risk
Most healthcare data breaches now originate with third-party vendors. You can run a secure network, train staff properly, and follow every HIPAA rule. Then a contractor gets compromised and your patient data ends up on the dark web anyway.
The problem is scope. You might work with dozens of software vendors and service providers. Each one touches protected health information or employee records. Some process billing. Others handle scheduling, communications, or HR functions. All of them create liability for your organization when they fail to protect data properly.
HIPAA holds you responsible for your vendors' security failures. The law calls them business associates, and you must ensure they protect data adequately.
What Vendor Auditing Actually Means
Auditing vendors does not mean accepting their security questionnaire and filing it away. It means actively verifying their security practices and monitoring them over time.
Start with basic due diligence before you sign any contract:
Request their most recent SOC 2 Type II report or equivalent security audit. If they do not have one, that tells you something important about their security maturity.
Ask about their incident response plan. How quickly do they notify customers after a breach? What support do they provide? Get specific commitments in writing.
Review their data handling practices. Where do they store your data? Who can access it? How long do they retain it? Do they use subcontractors, and if so, do those subcontractors meet the same security standards?
Check their insurance coverage. Do they carry cyber liability insurance? What limits? This matters when you need to recover costs after a breach.
Verify their compliance certifications. For healthcare vendors, look for HIPAA compliance statements backed by actual audits, not just claims on a website.
Put Requirements In The Contract
Your business associate agreement should include specific security requirements and audit rights. Standard BAA templates often lack enforcement mechanisms.
Include breach notification timelines. Thirty days is too long to wait for notification. Require notification within 24 to 48 hours of discovery.
Reserve the right to audit their security controls annually or after any security incident. Some vendors resist this, but it separates serious security providers from the rest.
Define data ownership clearly. When you terminate the relationship, how quickly must they delete your data? Can you verify deletion?
Specify encryption requirements for data in transit and at rest. Require multi-factor authentication for any staff accessing your data.
Include financial penalties for security failures. Vendors pay more attention to security when contract violations cost them money.
Monitor Vendors Continuously
Signing a good contract solves nothing if you never follow up. Most organizations sign vendor agreements and never look at security again until a breach happens.
Set calendar reminders to review vendor security annually. Request updated SOC 2 reports. Ask about any security incidents in the past year, even minor ones.
Monitor security news for breaches at your vendors. Subscribe to security newsletters or use breach notification services. You should not learn about your vendor's breach from the news.
Track vendor access to your systems. Review access logs quarterly. Remove access for vendor staff who no longer need it. Many breaches exploit old vendor accounts that nobody monitors.
Test vendor security with your own IT team. Can your staff access data they should not see in the vendor system? Do vendors disable accounts promptly when notified?
Review vendor performance during your regular security meetings. Make vendor risk a standing agenda item, not something you discuss only after problems emerge.
Create A Vendor Risk Register
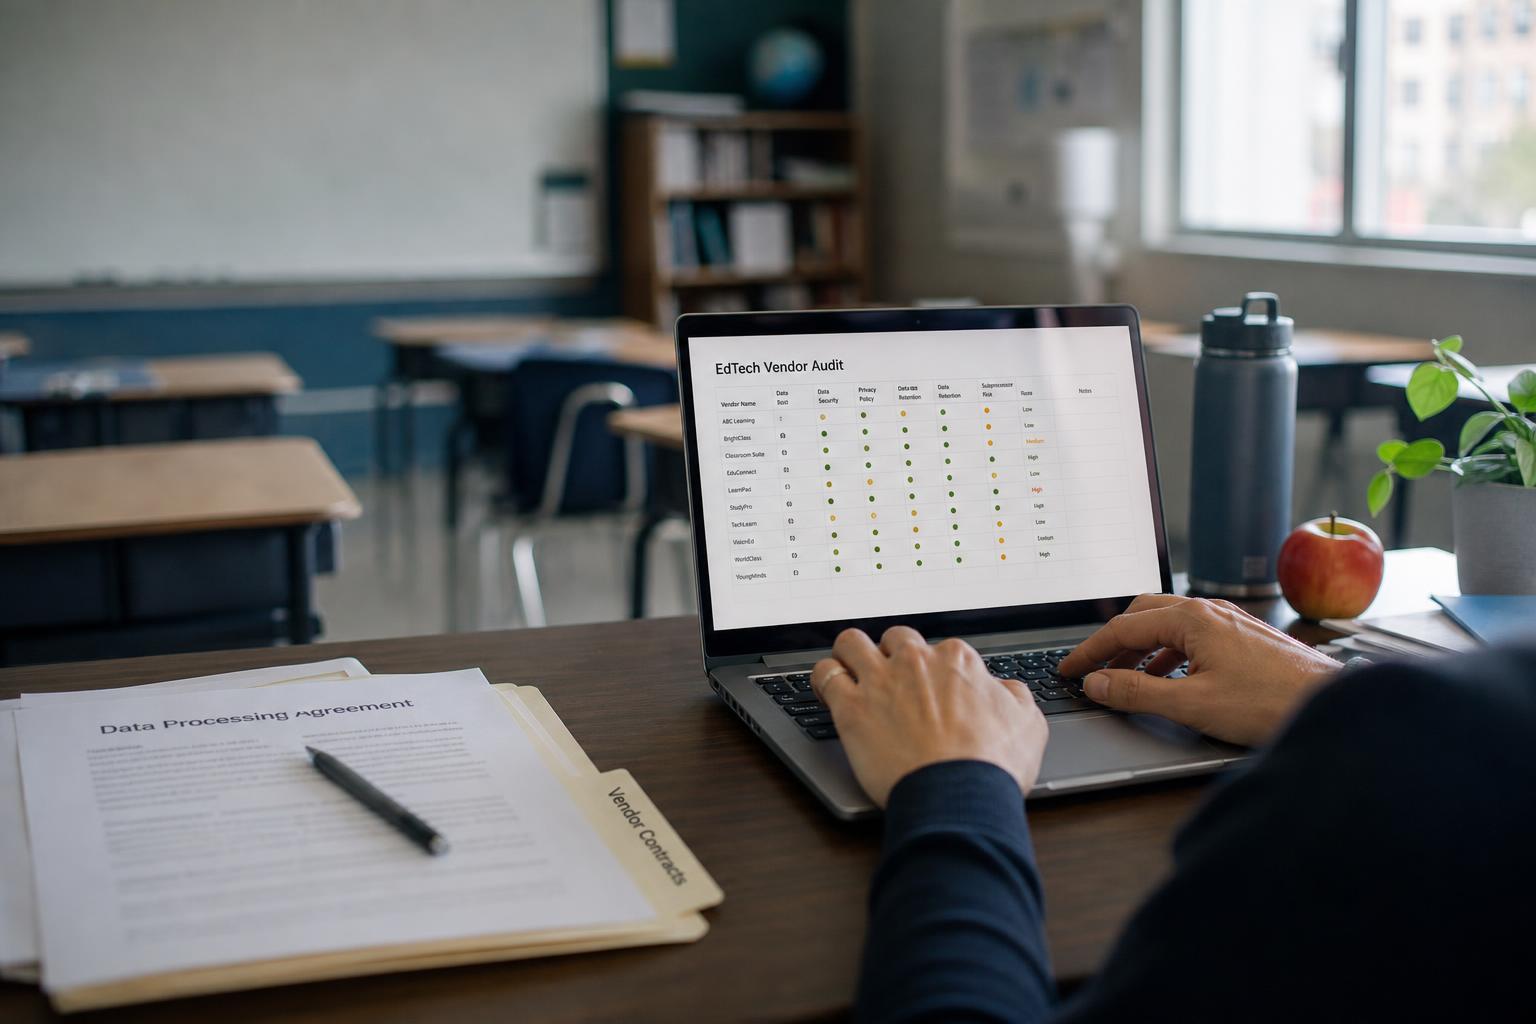
Document every vendor who touches sensitive data. Track their risk level, last audit date, contract renewal date, and any security concerns.
Rate vendors by the sensitivity of data they access and the likelihood of a breach. A billing vendor processing thousands of patient records rates higher risk than a vendor managing your office supplies.
Higher-risk vendors need more frequent audits and stricter contract terms. Lower-risk vendors still need oversight, just less intensive.
Update the register when you add new vendors or terminate relationships. Many organizations lose track of which vendors still have data access.
What To Do Right Now
Pull your vendor list today. Identify everyone with access to patient data or employee information. If you cannot list them all quickly, that itself is a security problem.
Contact your top five highest-risk vendors. Request their most recent security audit reports. If they cannot provide them within a week, escalate to management.
Review your business associate agreements. Do they include the security requirements and audit rights you need? Flag any gaps for your attorney to address at renewal.
Schedule vendor security reviews for the next quarter. Put them on the calendar now, or they will not happen.
Vendor breaches will keep happening. The question is whether you will learn about them from your audit process or from affected patients. Regular vendor security reviews cost time and effort, but they cost far less than breach response and regulatory penalties.
Not sure your IT is as solid as it should be? Take 10 minutes and tell us about your setup. No pressure, no obligation.
Book a 10-Minute Discovery Call →Last updated: November 4, 2026