Key points
- Phishing attacks are timed to land while people are distracted. Summer creates more of those moments.
- A single click can cascade across email, files, and shared systems before anyone notices.
- Telling employees to 'be more careful' is not a security strategy.
- Multi-factor authentication, email filtering, and least-privilege access limit how far one mistake can travel.
Your summer workday is a cybercriminal's favorite target
School's out. Your schedule shifted. Maybe you're starting earlier to finish before the kids wake up, or working from home with a dog barking and a toddler in the background. The workday is still happening. It's just happening in the gaps.
Cybercriminals know this. They don't wait for you to be careless. They wait for you to be busy.
Phishing emails (messages designed to trick you into clicking a malicious link or downloading a harmful file) aren't crafted to fool someone sitting quietly at a desk with nothing else going on. They're crafted to catch you mid-task: an invoice that looks routine, or a shared document from a name you half-recognize. Something that seems like it can be handled in two seconds.
When your attention is split, speed wins over scrutiny. That's the moment the click happens.
One click doesn't stay in one place
The click itself is only the start of the problem. What matters is what that account has access to.
Your email, your file storage, your accounting software, and your customer records are all connected. When an attacker gains a foothold through one account, they rarely stop there.
Malware (software designed to damage or gain unauthorized access to systems) can move quietly through your environment. It spreads to other accounts and pulls sensitive data or locks down files before anyone realizes something is wrong. By the time it's visible, the damage is already larger than a single mistake.
For a small business in Kyle, Buda, or San Marcos, that kind of incident is more than a bad week. It can mean lost client data and recovery costs that weren't in the budget, with regulatory exposure on top depending on what was taken.
Why 'just be more careful' is not a security plan
It's tempting to respond to this risk with a reminder to slow down and double-check everything. The advice is fine. It just doesn't get you very far on its own.
Your team is juggling conversations and switching tasks all day to keep things running. Expecting perfect attention on every email and every attachment doesn't match how real workdays go, especially in summer.
Security that depends on nobody ever making a mistake will eventually fail. The goal should be systems that limit the damage when a mistake happens, because it will.
What reduces your risk
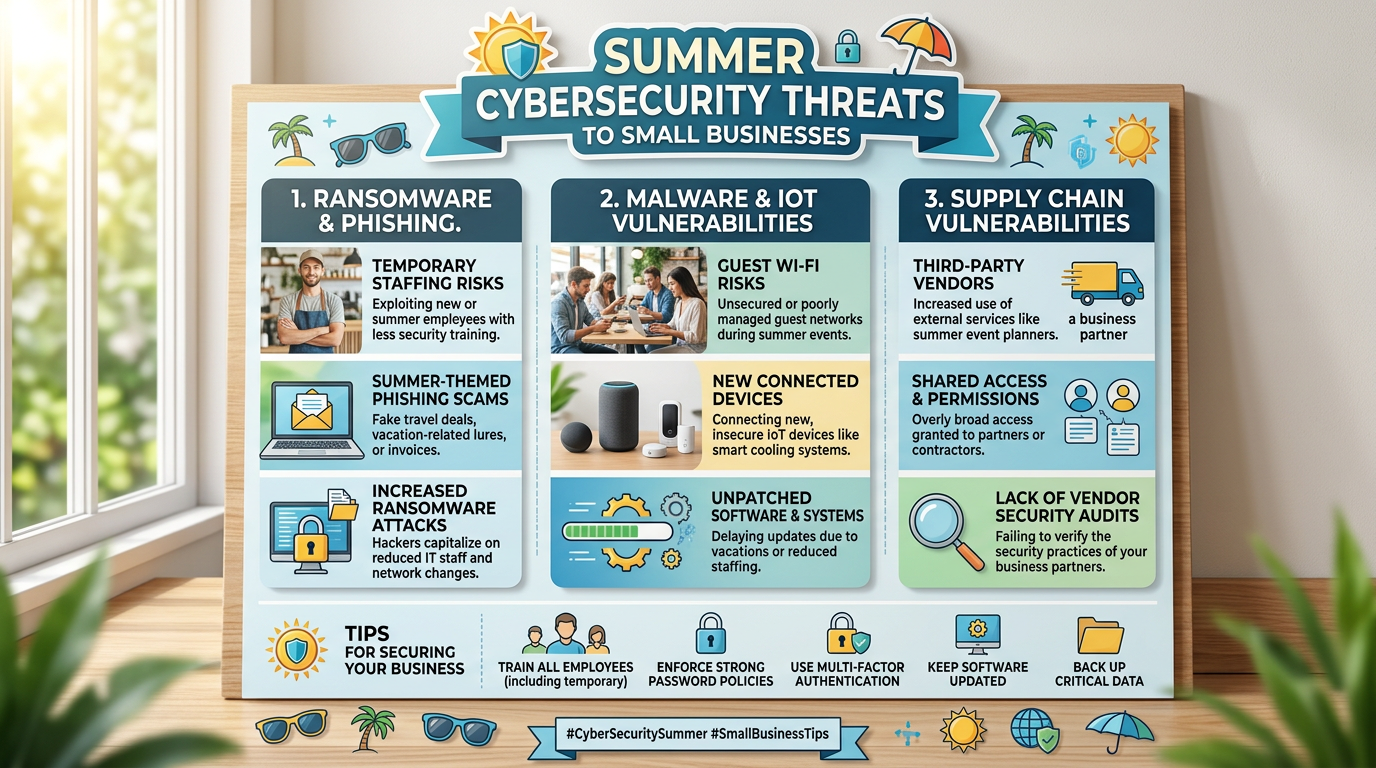
Good security assumes your team will be distracted and moving fast. Guardrails do the work that attention can't. In practice, that means:
- Unique passwords for every account. If one login is compromised, it shouldn't unlock everything else. A password manager makes this manageable without slowing anyone down.
- Multi-factor authentication (MFA). MFA means a stolen password alone isn't enough to get in. The attacker also needs a second verification step, like a code sent to your phone. Turn this on everywhere it's available, especially email and financial accounts.
- Email filtering. Suspicious messages should be flagged or blocked before they reach your team's inbox. Fewer risky decisions get made when fewer risky emails arrive.
- Least-privilege access. Employees should only have access to the systems and files their job requires. This limits how far a compromised account can reach.
- A low-friction way to ask 'does this look right?' When something feels off, your team needs to be able to pause and check, without feeling like they're slowing things down or overreacting.
None of these depend on flawless behavior. They're built for the workday as it is.
The question to ask before something goes wrong
If someone on your team clicks the wrong link this afternoon, is that a minor inconvenience, or something that spreads across your systems before end of day?
Would you catch it within minutes, or only after the damage is done?
These weak spots exist year round. Summer makes them easier to miss because everyone is moving faster and paying less attention to the background.
If your business still relies on everyone catching everything perfectly, that's worth addressing now, before the pace picks up again in the fall.
At safemode IT, we're based in Kyle, TX and can be on-site across Hays and Bastrop counties within 30 minutes. If you want to know how exposed your business is, a quick conversation is a reasonable place to start. There's no pressure and no sales pitch.
Not sure your IT is as solid as it should be? Take 10 minutes and tell us about your setup. No pressure, no obligation.
Book a 10-Minute Discovery Call →Frequently asked questions
Why are phishing attacks more effective during summer?
Summer disrupts routines. People work from home more, manage childcare alongside work, and handle tasks in shorter, interrupted stretches. Phishing emails are designed to catch people mid-task, when speed tends to win over scrutiny. More distraction means more of those vulnerable moments throughout the day.
What is multi-factor authentication and does my small business really need it?
Multi-factor authentication (MFA) requires a second verification step, usually a code sent to your phone, in addition to your password. Even if an attacker steals your password, they can't log in without that second factor. For a small business, MFA on email and financial accounts is one of the cheapest and most effective security steps available.
How far can one phishing click spread inside a small business?
It depends on how your systems are set up. If accounts share passwords, if employees have broad access to files and systems, or if there's no monitoring in place, a single compromised account can give an attacker access to email, documents, client records, and more. Limiting access and enabling MFA are the two fastest ways to contain that exposure.
What should I do if I think an employee clicked a phishing link?
Act quickly. Disconnect the affected device from your network if possible, change the passwords for any accounts that were open or recently used, and notify your IT provider immediately. The faster you respond, the more you limit how far the attacker can move. If you don't have an IT provider on call, that gap is worth closing before an incident happens.
Can safemode IT handle this for us if we are not in Kyle, TX?
Yes. We serve small businesses throughout Hays and Bastrop counties, including Buda, San Marcos, Bastrop, and the Austin area, and on-site response across that area is typically within 30 minutes. Learn more about our managed IT services or reach out to start the conversation.
Last reviewed and updated: June 8, 2026
Last updated: June 8, 2026