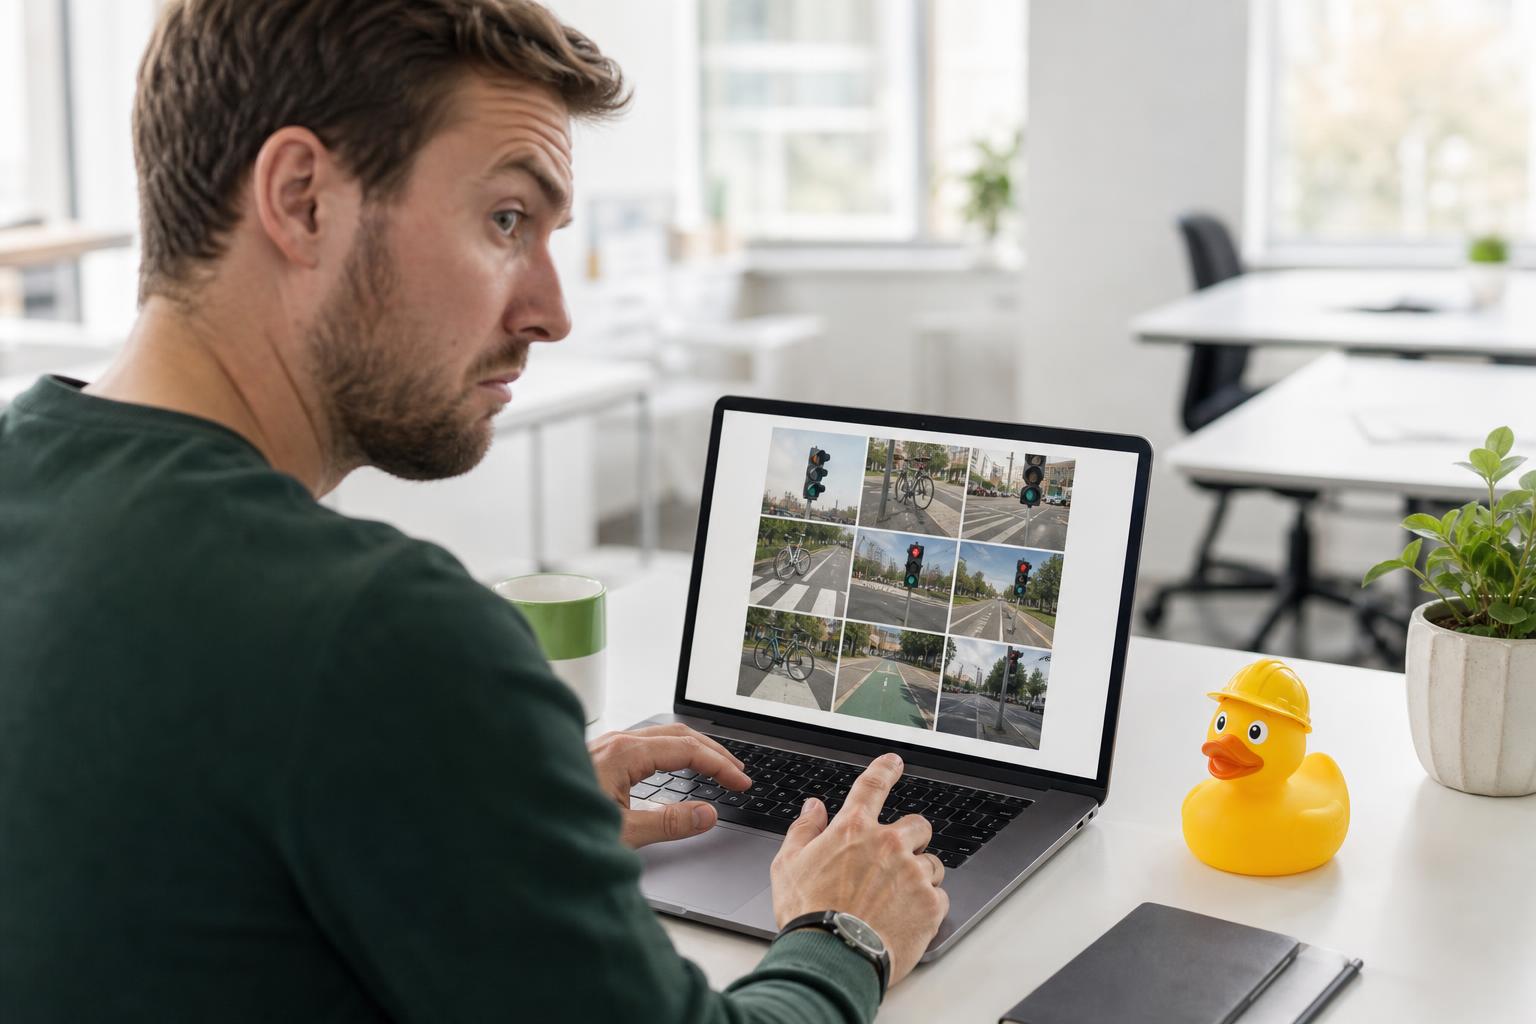
You land on a page that wants proof you are human. Fine. Then the instructions tell you to press the Windows key plus R, paste something, and hit Enter. That is not a CAPTCHA. That is a stranger asking you to run their code on your computer.
The attack has a name, ClickFix, and it works because the steps feel like IT troubleshooting. This tip covers how it works and the one rule that stops it.
How ClickFix works
Attackers put a fake verification prompt on a compromised website. It looks like the usual check, but instead of clicking traffic lights you are told to open the Windows Run dialog, paste a command, and press Enter. The command is typically PowerShell, according to a security notice from McMaster University.
The page often copies the command to your clipboard for you, so you may never see what you are about to run. Because you launch it by hand, the whole thing can look like normal user activity instead of a download, which is part of why it slips past people and some tools.
The one rule
A real CAPTCHA never asks you to open Run, PowerShell, or Terminal. McMaster's security team puts it plainly: if a website, CAPTCHA, email, or Microsoft Word pop-up asks you to press the Windows key plus R, or to open PowerShell and paste and run code, it is highly likely a ClickFix attack.
Tape that sentence to a monitor if you have to. It covers every variation of the trick.
If someone already did it
Do not close the tab and hope. Disconnect the computer from the network, tell IT right away, and change passwords from a different device. A command pasted into Run can install malware, so the computer needs a proper check before anyone trusts it again. Speed matters more than embarrassment, and nobody at your company should be teased for reporting this.
Cut down the damage
Staff should not run day to day with local administrator rights, since that limits what a pasted command can do. Managed endpoint protection adds a second chance to catch the payload. Neither replaces the rule above, but both shrink the blast radius when someone slips.
The bigger lesson
Attackers have figured out it is easier to talk you into doing the work than to break in. The defense is a habit your team repeats without thinking, backed by tools that assume someone will eventually click. That combination is what we build for clients under our managed IT services.
Most breaches start with one person helping the wrong stranger. We train staff and lock down endpoints so one bad click does not become a bad month. No pressure, no obligation, just a straight look at your setup.
Book a 10-Minute Discovery Call →Frequently asked questions
What is a ClickFix attack?
It is a social engineering attack that shows a fake verification or error page and tells you to copy, paste, and run a command yourself. The command is typically PowerShell, launched from the Windows Run dialog.
Would antivirus stop it?
Sometimes, but not reliably. Since you run the command yourself, it can look like ordinary activity. Good endpoint protection helps, and the human rule still matters most.
Does this only affect Windows?
The version described here uses the Windows Run dialog, so Windows is where it shows up most in security notices.
What should I do if I already pasted the command?
Disconnect from the network, tell IT immediately, and change your passwords from another device. Do not keep working on that computer until someone has checked it.
Can safemode IT train our staff and lock this down?
Yes. We combine short staff training with endpoint protection and admin-rights cleanup. See our managed IT services or ask for a free assessment.
Source: McMaster University, IT Notice on ClickFix attacks
Last updated: October 8, 2026